Kyūdō
The AI layer

AI that holds up under audit, regulator, and board scrutiny.

Confident language is not assurance. If an AI tells you a control is satisfied, the right next question is: based on what? Which evidence? Which framework citation? At what confidence?

An AI that can’t answer those questions doesn’t belong near a regulator. Generative fluency is not traceable reasoning. In regulated governance, the explanation is the product.

Kyūdō's AI is not a wrapper on a large language model. It's a retrieval discipline with explicit provenance on every response. Every output is grounded in Compliance Graph entities, scored for confidence, and cited to its source.

So AI artifacts survive the auditor's next question, and the EU AI Act Article 13 reviewer's first one.

Auditor query
> Show me the privileged-access posture for AC.L2-3.1.6 and any drift in the last 24h.
Retrieval trace
01Resolve control AC.L2-3.1.6 · SOC 2 CC6.1
02Pull evidence entra.identity · 14:22 UTC
03Crosswalk frameworks AC.L2-3.1.6 · SOC 2 CC6.1
04Score confidence 0.94 · above threshold
Sensei response
confidence 94%

Conditional access state for privileged role activation satisfies AC.L2-3.1.6 and partially satisfies SOC 2 CC6.1. Evidence refreshed at 14:22 UTC from Entra ID; lineage is intact.

One residual gap: privileged session lifetime exceeds the policy ceiling on 2 of 14 roles. Routed to the policy owner with Policy Center → policy.v3.4 for remediation draft.

Grounded in your actual records

Every recommendation retrieves specific controls, evidence, risks, or policies from the graph before generating. The compliance graph nodes used are returned with the answer.

retrieve → cite → generate

Confidence scoring on every output

When the AI isn’t confident, Kyūdō says so, and routes the question to a human before it lands in a report, an audit package, or a customer response. You never find out after the fact that an AI guess became your official position.

confidence threshold · 70%

Citations on every clause

A skeptical auditor can open any AI artifact and follow the reasoning to its source nodes, framework clauses, and evidence items, and reproduce the same trace on demand.

deterministic retrieval

Prove a control once. Reuse it across every framework that needs it.

Add SOC 2, ISO 27001, HIPAA, CMMC, or the EU AI Act and Kyūdō knows which controls you already satisfy, which need work, and which need new evidence. You stop paying to prove the same thing five different ways.

NIST standard for cross-framework mapping

The receipts are already there.

When the regulator, board, or auditor asks how an answer was produced for the EU AI Act Article 13, or a CMMC control, Kyūdō already has it: sourced, timestamped, and tied to the system that generated it. Nothing to assemble. Nothing to reconstruct.
EU AI Act Art. 13
EU AI Act · ISO 42001 · NIST AI RMF
Govern the AI you deploy - with the platform that runs inside your tenant.
Explore AI Governance
AI Copilot

Your team's compliance workload, cut by up to 75%.

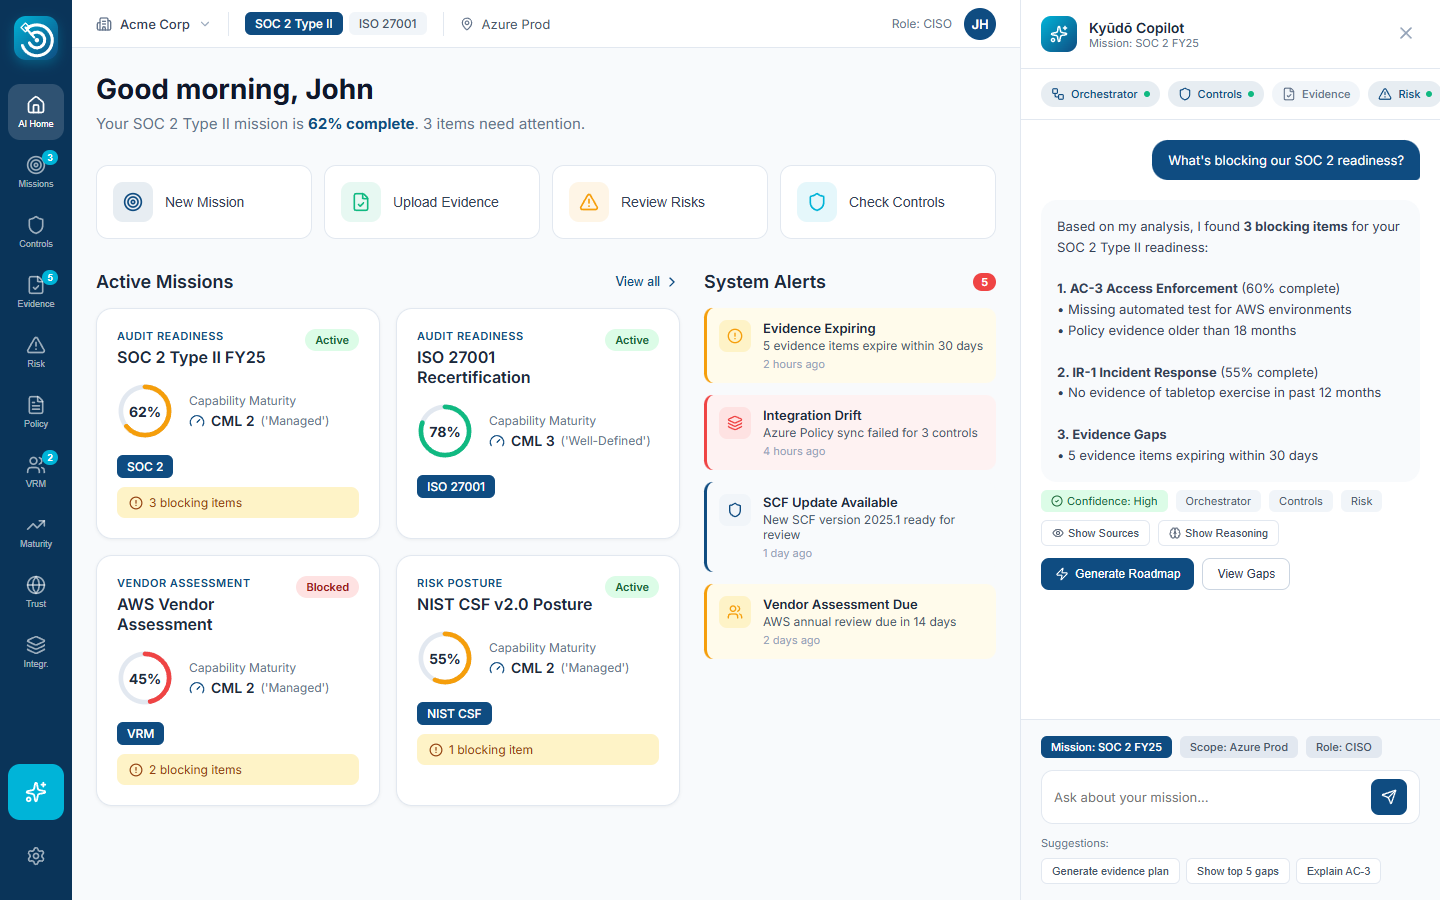
The hidden cost of compliance isn't the audit. It's the thousands of hours your team spends drafting policies, chasing evidence, and answering the same vendor questionnaires repeatedly. Sensei eliminates most of that work. Policies drafted in minutes. Vendor questionnaires answered automatically from your control library. When a regulator asks how the AI reached its conclusion, Sensei shows them, with a full evidence chain tied to your actual data.

Sensei AI Advisor
Sensei AI Copilot home
Key Capabilities

Built for how compliance actually works.

Policy creation time cut by up to 75%

AI-assisted drafting grounded in your existing controls and active frameworks. Policies that took days to produce take minutes.

Vendor questionnaire cycle from days to under an hour

Sensei drafts responses automatically from your live control library. Every answer cites the controlling evidence. Human reviewers approve in minutes.

Every AI output carries a confidence score and provenance chain

Regulators and auditors can trace every recommendation back to the source document, control record, or evidence item. No black-box outputs.

Your compliance data stays in your tenant

Sensei's reasoning is grounded in your Compliance Graph, not generic LLM training data. Your evidence never leaves your environment or improves someone else's model.

01

Missions: Structured AI Workflows With Human Checkpoints

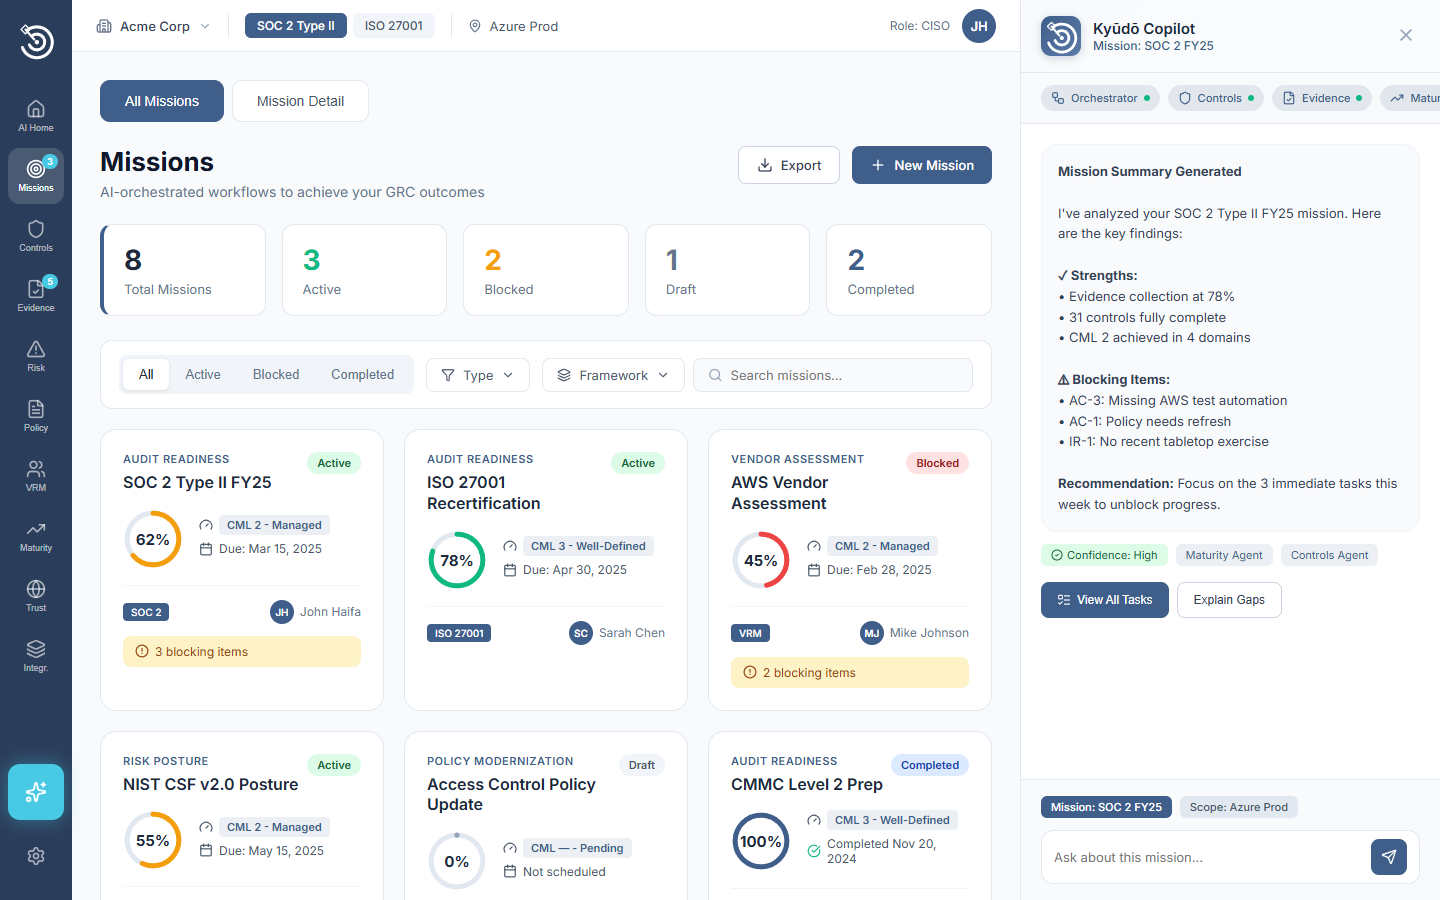
Missions are multi-step compliance workflows that Sensei executes with human approval at each critical decision point. A policy review, a risk assessment, a vendor questionnaire response cycle, all handled end to end. The Mission Launcher queues, executes, and logs every step. Audit trails are generated automatically. Nothing moves forward without a human sign-off.

Missions
Mission Launcher view
02

From Prompt to Compliance Artifact in Minutes

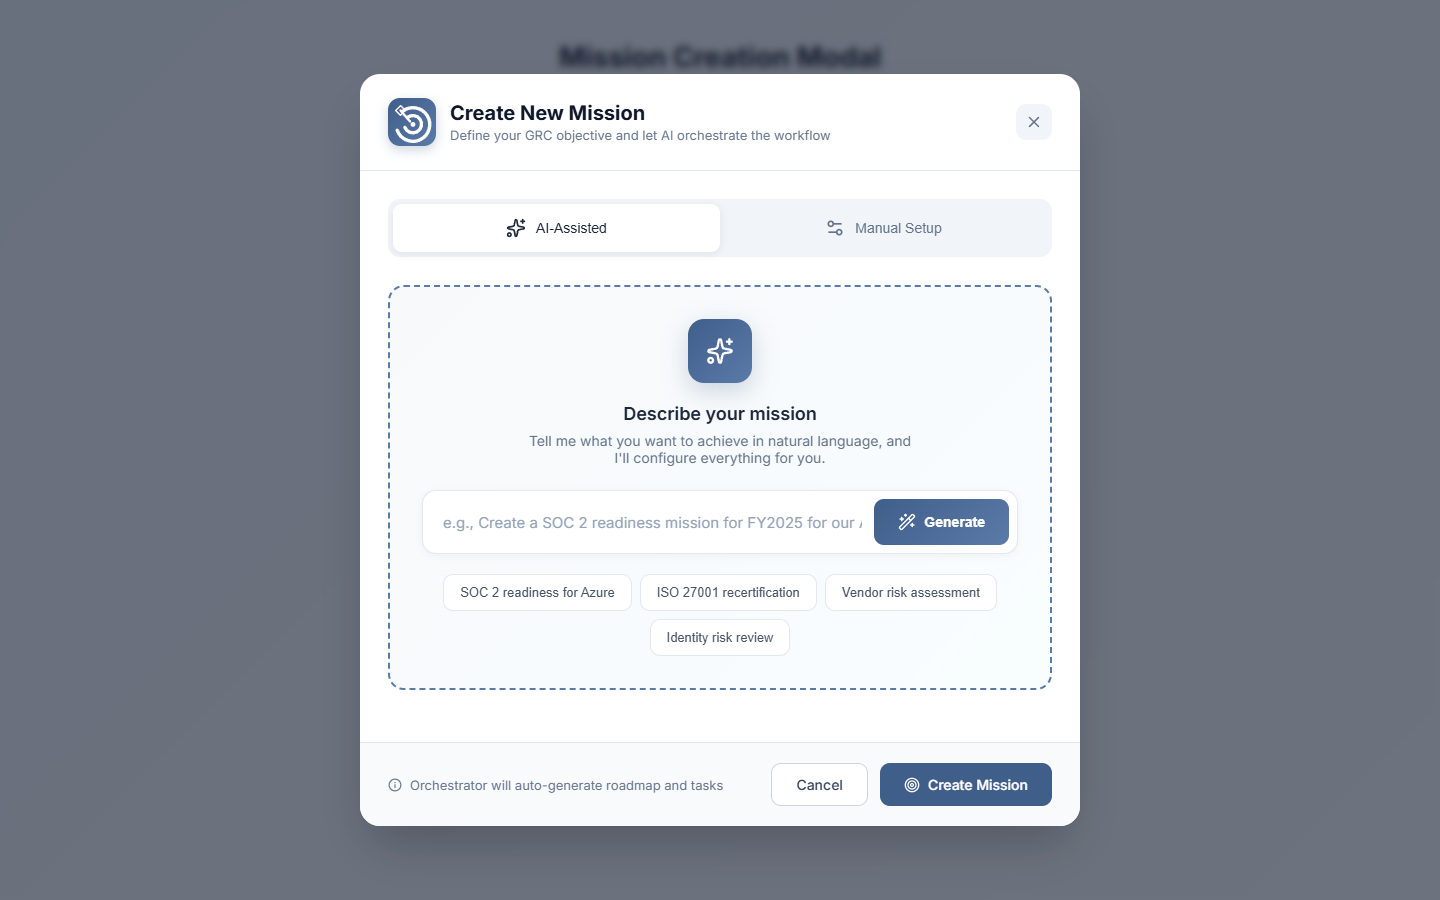
Creating a mission takes seconds: describe the objective, select the relevant Sensei role, and attach the scope. Sensei drafts the plan, identifies the required evidence, and flags any confidence gaps before execution begins. Human review is built into the flow, not added after. Every artifact produced carries full provenance metadata.

Mission Creation
Mission creation workflow